01
Penetration Testing
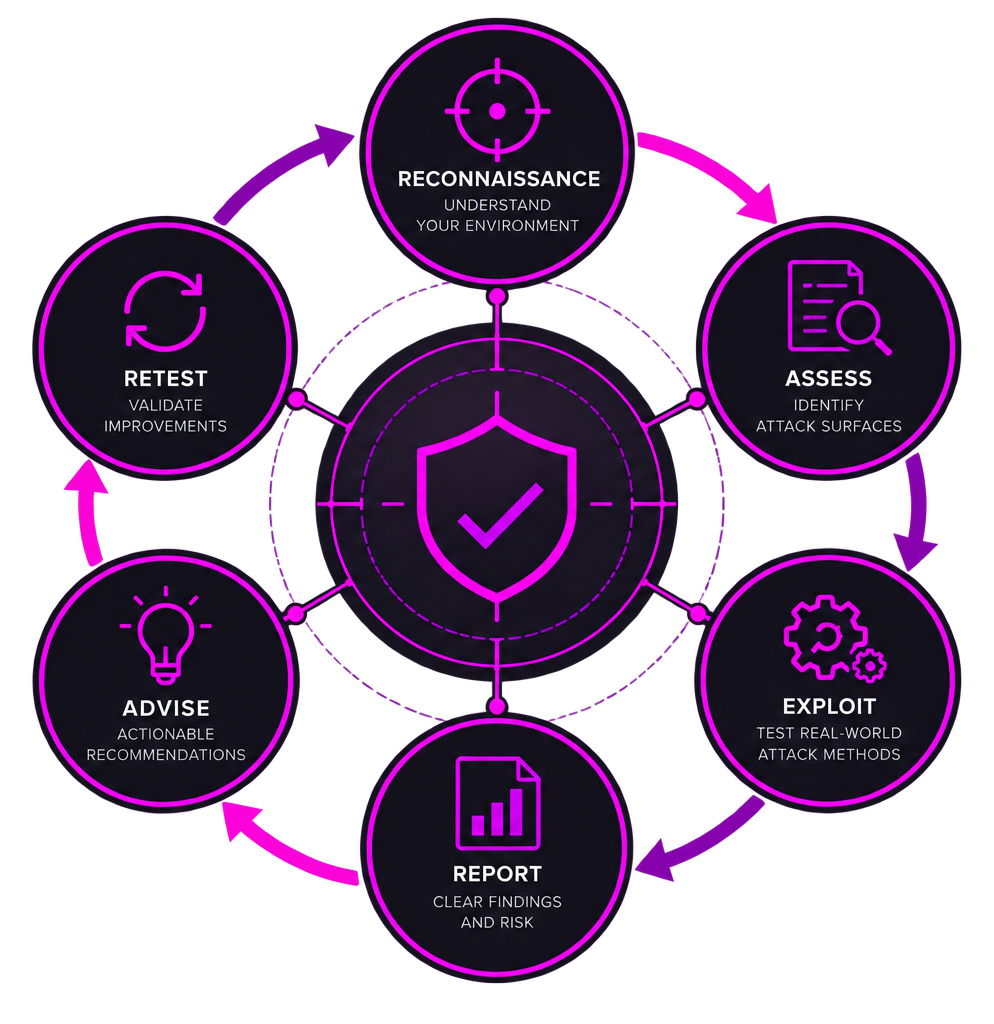
We simulate real-world attacks against your applications, infrastructure and external attack surface to uncover exploitable vulnerabilities before attackers do.

Services
Independent penetration testing, security audits and bespoke security assessments designed to give you a clear understanding of your exposure, the risks that matter, and the evidence to act on them.
Our services
Our security assessment services help you understand your true level of risk. We provide independent, expert analysis of your security posture, giving you clear visibility of vulnerabilities, weaknesses and areas for improvement.
The result is actionable insight that enables you to make informed decisions, prioritise security investment and demonstrate confidence in the controls that protect your organisation.
Whether the goal is assurance, compliance or risk reduction, we help you focus on what matters most and take practical steps to strengthen security.
What we do
We help organisations understand where they are exposed, how attackers could get in, and what to do about it. Our work is practical, independent, and led by experienced security professionals.
01
We simulate real-world attacks against your applications, infrastructure and external attack surface to uncover exploitable vulnerabilities before attackers do.
02
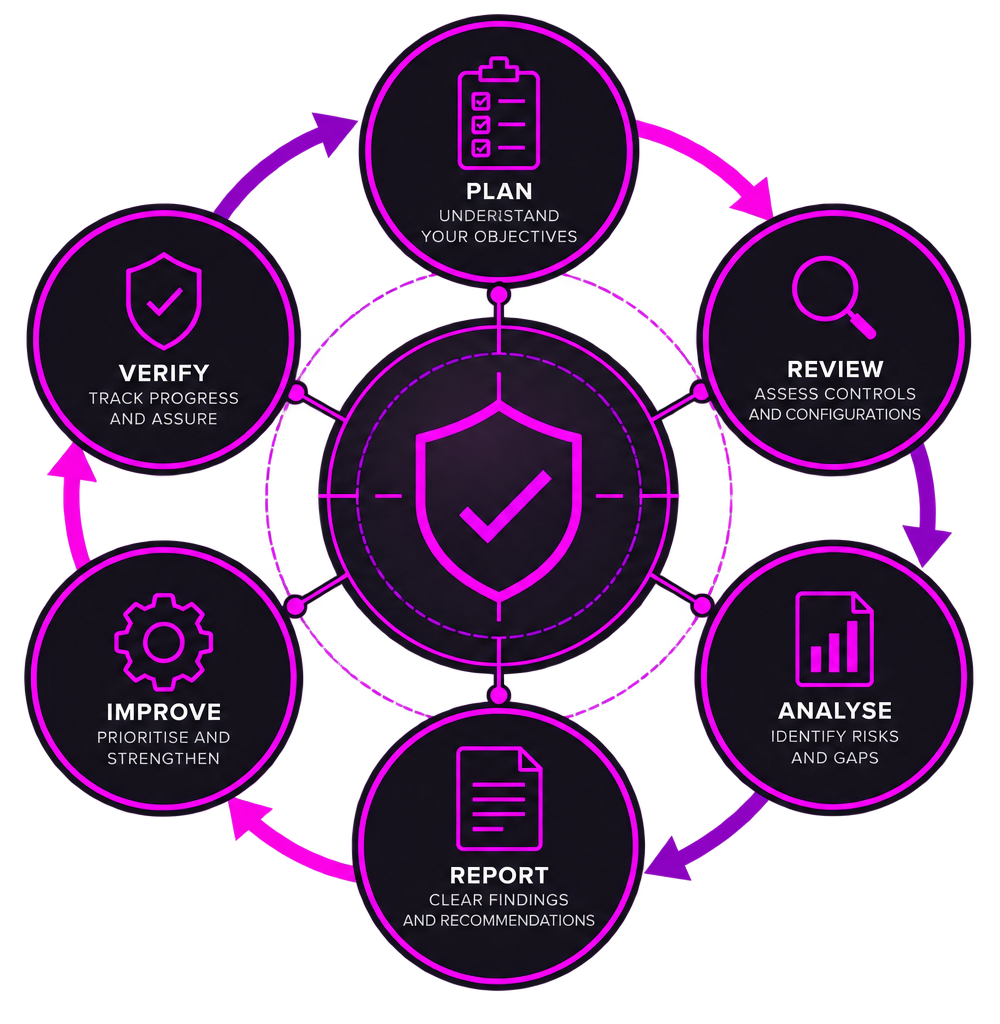
Independent assessments of your security controls, architecture and processes, giving you a clear view of weaknesses, risk and where improvements will have the greatest impact.
03
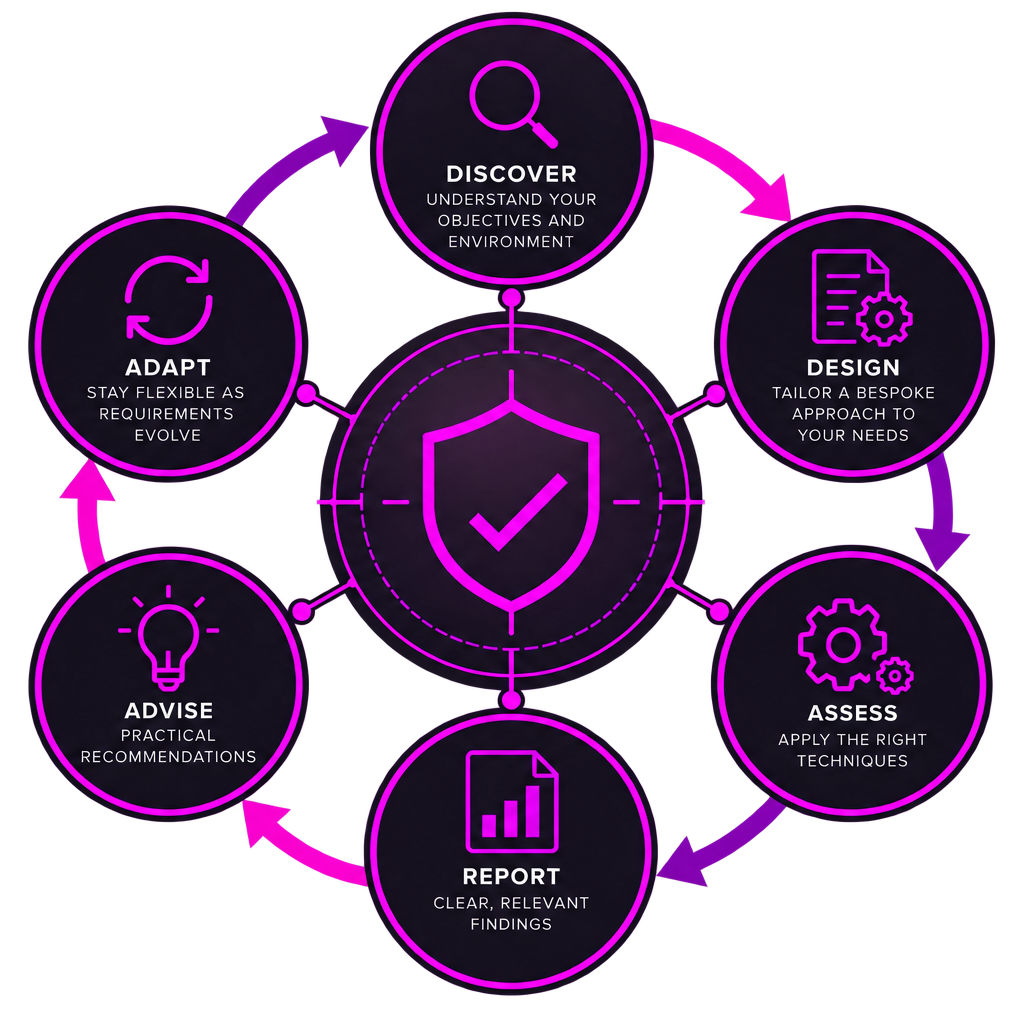
Focused security testing built around a specific objective, concern or attack scenario, providing independent evidence and insight where a standard test may not be enough.
Find out what an attacker could actually do. We combine established methodologies, automated tooling and manual testing to uncover vulnerabilities and demonstrate realistic attack paths.
Understand how well your security controls stand up to scrutiny. We assess your configuration, architecture, processes and controls against your requirements, identifying weaknesses and prioritising the improvements that matter most.
Not every security question fits a standard test. We design focused assessments around your objectives, investigating specific concerns, systems, controls or attack scenarios.
Assurance & certification
From NCSC CHECK penetration testing to Cyber Essentials certification, we help organisations meet security requirements and demonstrate their security posture.
01
Expert-led penetration testing aligned with NCSC CHECK requirements for infrastructure and web applications.
02
Practical consultancy and readiness support to help you meet the Cyber Essentials requirements and prepare for certification.
03
Readiness assessment and technical preparation for the additional verification required by Cyber Essentials Plus.
Assessment approach
Every engagement is shaped around your objectives, environment and risk. We will recommend the approach that gives you the most useful evidence, without adding unnecessary scope.
| Approach | Focus | Best for | Outcome |
|---|---|---|---|
| Penetration test | Exploitable vulnerabilities and attack paths | Understanding what an attacker could achieve | Validated findings, evidence and recommendations |
| Security audit | Controls, configuration, architecture and processes | Assessing security posture and identifying weaknesses | Risk-based findings and recommendations |
| Objective-led assessment | A specific security question or scenario | Testing a particular concern, control or attack path | Evidence against defined objectives |
| NCSC CHECK testing | Infrastructure and web application penetration testing | Meeting requirements for government, public sector and CNI assurance | CHECK-aligned testing, findings and formal reporting |
| Cyber Essentials | Five core technical security controls | Improving baseline security and achieving certification | Certification readiness and practical security improvements |
| Cyber Essentials Plus | Cyber Essentials controls and independent technical verification | Organisations requiring stronger assurance | Certification readiness and independent technical assessment |
| Retest | Previously identified vulnerabilities | Verifying that remediation has addressed the findings | Independent remediation assurance |
| Periodic assessment | Annual penetration tests and recurring vulnerability assessments | Maintaining visibility as your environment changes | Regular evidence of your security posture |
Note
No two environments are the same, so we do not force every engagement into a standard package. Testing can be conventional, objective-led, or a combination of both, with scope and boundaries agreed before work begins.
Describe the problem and we will tell you where we would start.